You can find this feature in the "Access Control" tab of a site's configuration.
You'll be able to see a quick sum up of the access rule and be able to either enable it or disable it, edit it or remove it.
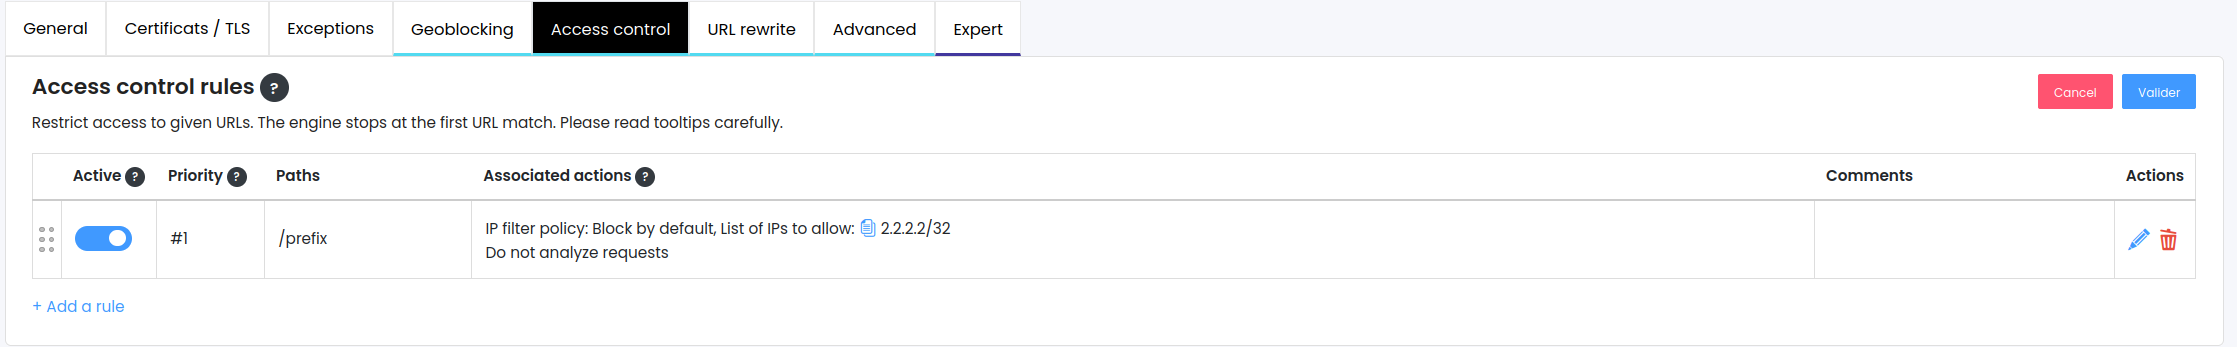
Within the same configuration you can set multiple type of different rules:

Paths
The list of paths the rule applies to. Regular expressions are supported (see the linked regex guide).
Type a path and press Enter or Tab to add it. You can also paste a list of paths (one per line), invalid entries are discarded and duplicates removed. At least one path is required to save the rule.
IP filtering
Choose a default policy for the matched paths:
Allow: traffic is accepted, and the exceptions list becomes the list of blocked IPs.
Deny: traffic is refused, and the exceptions list becomes the list of allowed IPs.
Exceptions accept single IP addresses or CIDR ranges; a single address is normalized to its /32 (or /128) form. Paste of multiple entries is supported, invalid values are ignored.
Analysis
Enables or disables the security analysis on the matched paths. When disabled, requests bypass inspection entirely.
Challenge
Adds a challenge on the matched paths before the request reaches the origin. The selector is disabled when the analysis is turned off.
Cache
Enables caching on the matched paths. The toggle stays disabled until caching is activated at the site level.
Custom error pages
Selects the profile used to render error and challenge pages for the matched paths. Only shown when at least one custom pages profile exists on the site and your account has the corresponding permission.
Comment
Free text field to document the intent of the rule.